
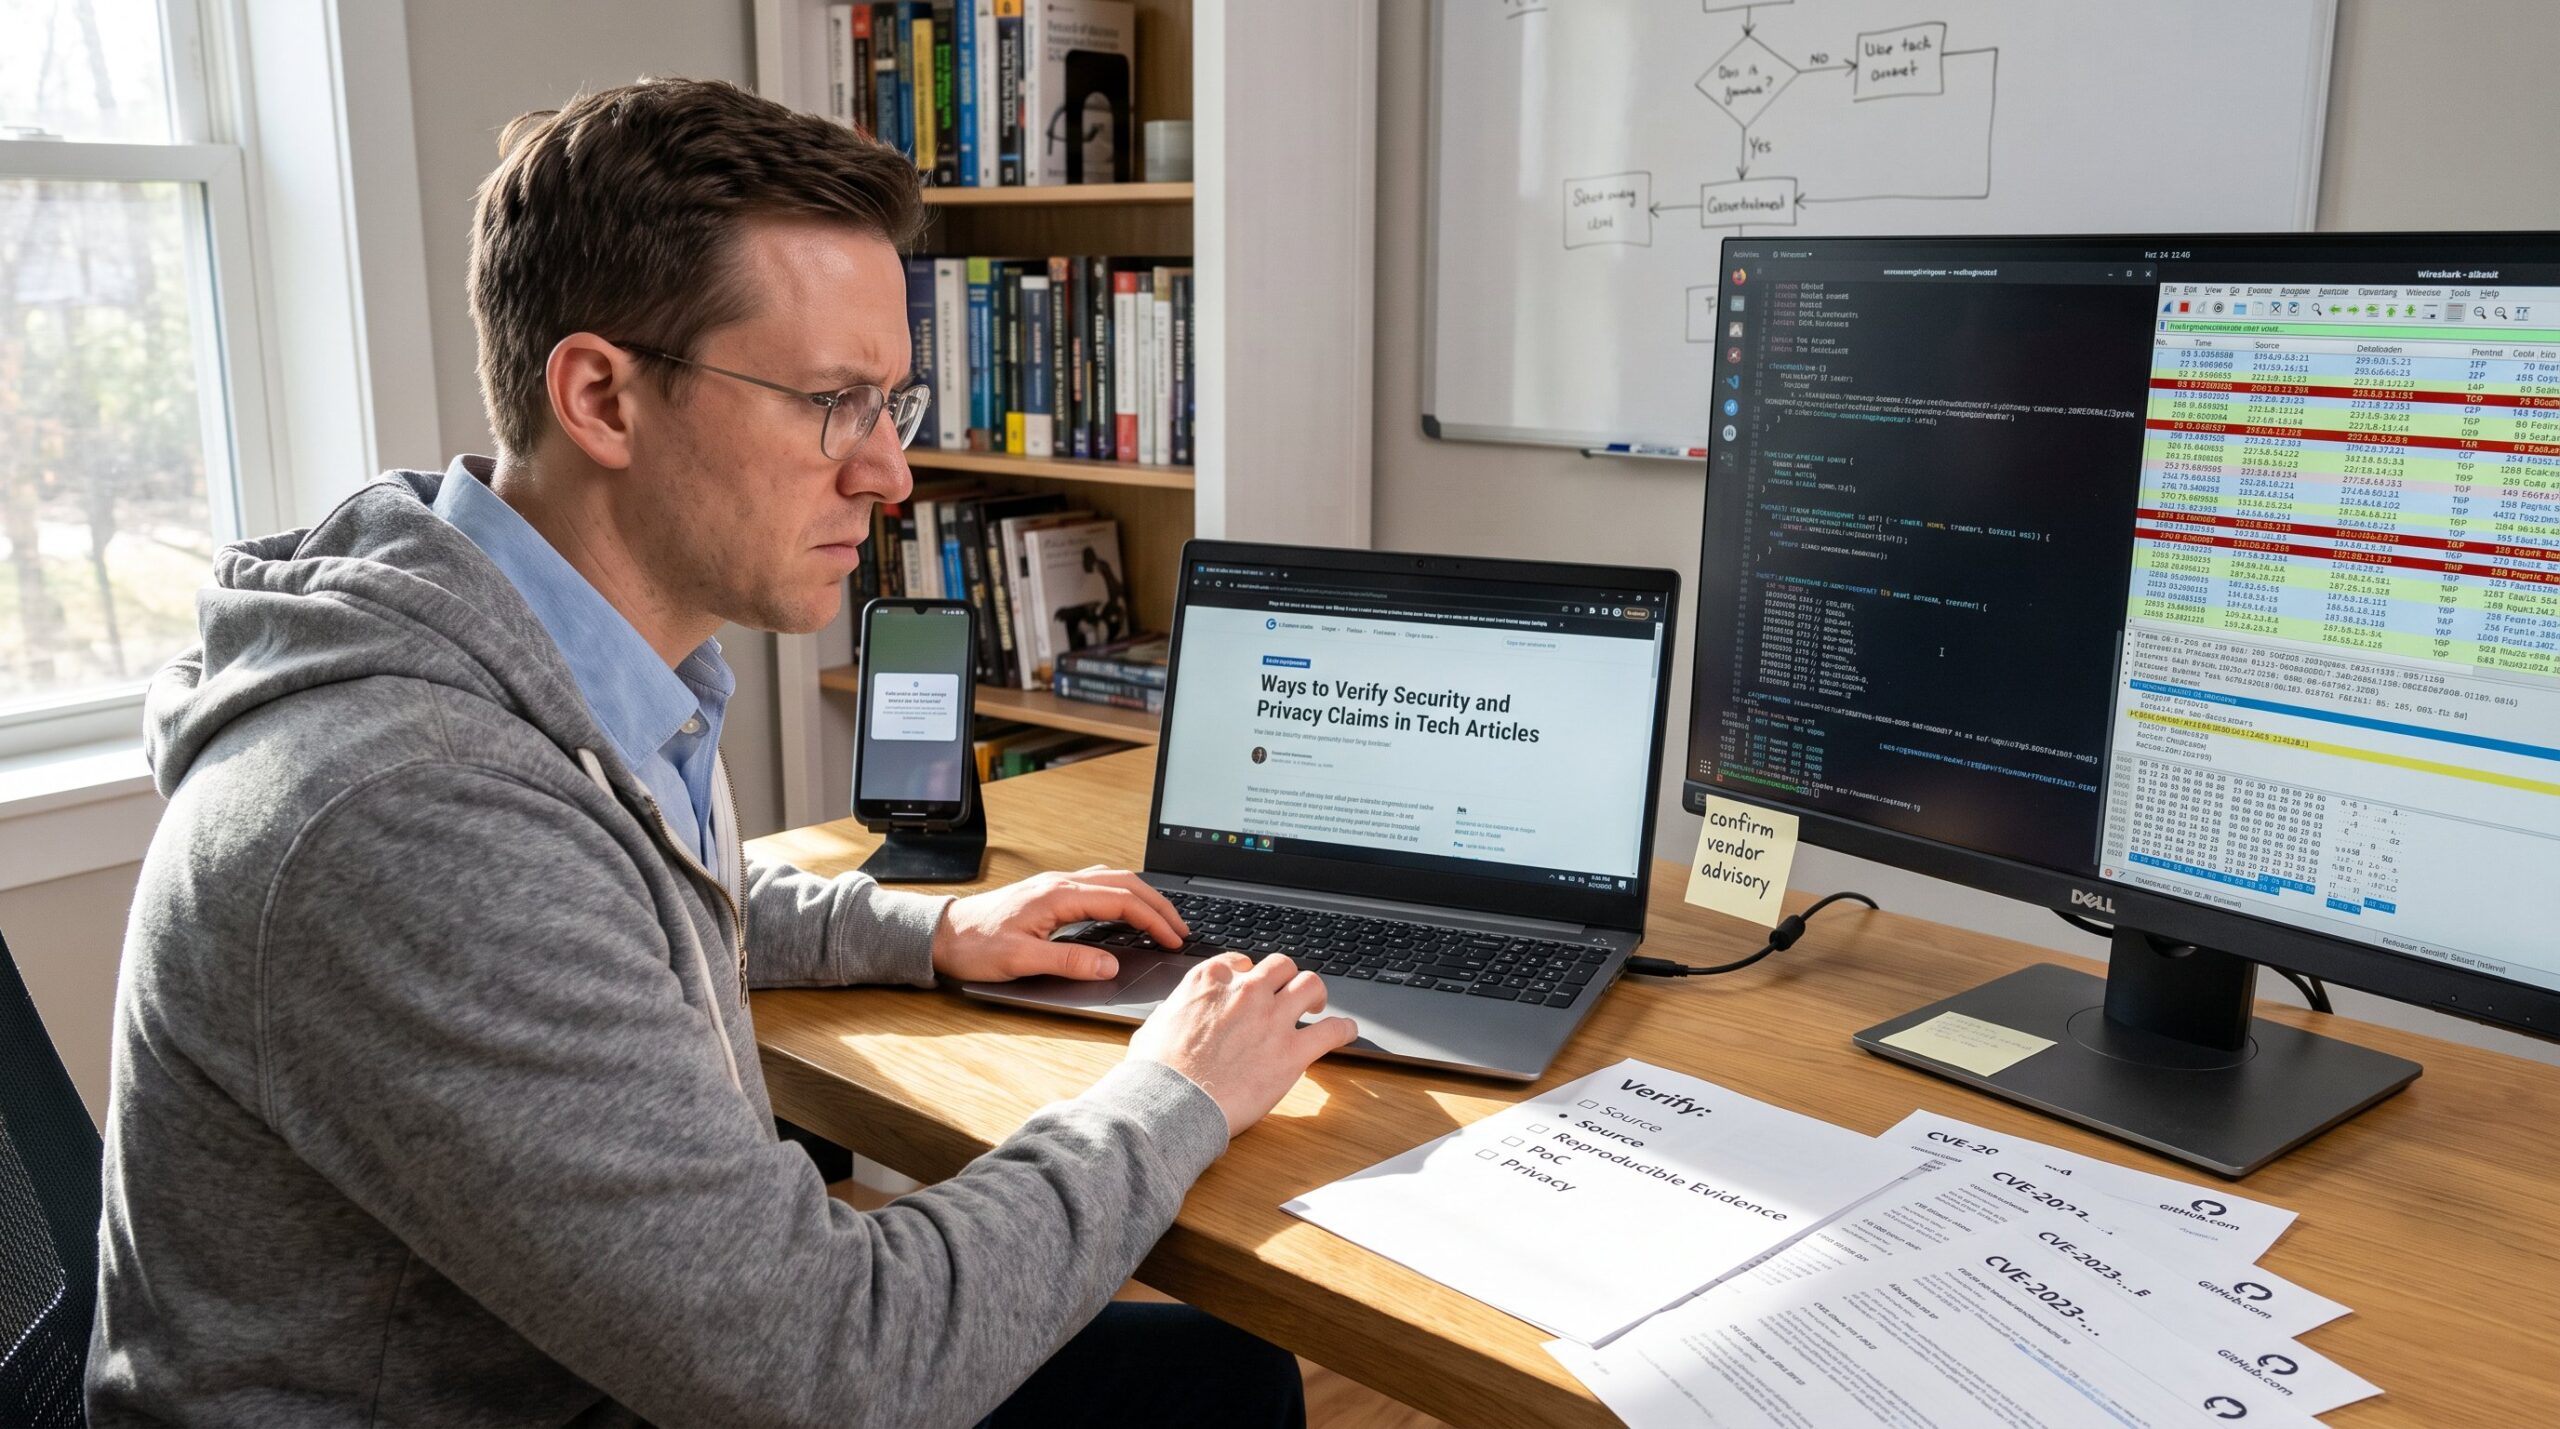
Ways to Verify Security and Privacy Claims in Tech Articles appears in many headlines, but readers need practical checks. This piece gives a compact, executable checklist. It places the core fact up front: verify claims by checking source credibility, reproducible evidence, clear vulnerability proofs, and transparent privacy practices. The guide suits analysts, product teams, and curious readers who must decide when to trust a report and when to demand proof.
Key Takeaways
- Verify security and privacy claims by assessing source credibility, including author profiles, publication reputation, and disclosure of conflicts of interest.
- Technical claims must include reproducible evidence with clear methodology, specific tool versions, and accessible artifacts for independent validation.
- Strong vulnerability reports provide explicit impact descriptions, reproducible proofs of concept, and responsible disclosure timelines to ensure trustworthy findings.
- Privacy assertions require confirmation through published policies, examined permission requests, network data flows, and alignment with relevant regulations like GDPR or CCPA.
- Applying a thorough verification checklist helps readers distinguish verified security and privacy facts from unproven hypotheses, enhancing trust and informed decision-making.
Spot Red Flags Fast: Assess Source Credibility
Fact first: the fastest way to discard dubious claims is to test source credibility. Start by checking the author’s identity and history. Does the byline link to a real profile with past reporting, technical posts, or cited research? If the author has a pattern of corrections or vague bios, treat dramatic claims as unproven.
Next, examine publication signals. Established tech outlets often show editorial contacts, corrections, and sourcing norms. A freshly created blog or anonymous post with sweeping assertions is a red flag. Look for clear citations: links to primary documents, vendor advisories, CVE entries, or academic papers. Articles that make legal or technical claims without any traceable source should be questioned.
Check conflicts of interest and funding. Does the article promote a product, a service, or a startup without disclosure? Transparency matters: undisclosed vendor relationships weaken credibility. Also spot coordinated amplification: many identical posts across different accounts can indicate a seeded marketing push or disinformation campaign.
Practical checks: verify the domain age and WHOIS ownership for unknown sites: search the author’s past bylines for accuracy: and confirm whether other respected outlets report the same finding. For step-by-step vetting of the tech beat, readers can compare methods with FeedBuzzard’s overview of broader trends in wearables and digital tech, which models clear sourcing and topic context in reporting about devices and datasets, as found in a related tech overview guide.
Verify Technical Claims: Reproducible Evidence, Methodology, And Tools
Fact first: credible technical claims include reproducible steps, tool lists, and precise versions. A good article names the exact product version, the configuration used, and the inputs that produced the observed result.
What to look for in methodology: a clear test setup (OS, firmware, software build), the commands or scripts used, and expected outputs such as logs or response codes. If a report omits versions and setup details, independent verification becomes impossible. Reproducibility matters: testers should be able to repeat the steps and see equivalent results in a similar environment.
Tools and artifacts increase trust. Authors who publish code snippets, sanitized datasets, packet captures (pcap), or terminal transcripts make independent checks feasible. If the article links to a GitHub repo or offers downloadable artifacts, spot-check the repository: is it recent, does it contain test data, and are there instructions? Beware of repositories that contain placeholders or only screenshots without the underlying test code.
Applied example: when an article claims a wearable leaks health data, it should list the device model, firmware (e.g., v2.3.1), and the API endpoints queried. If the report includes a reproducible curl command or a short Python script and expected JSON output, an independent reviewer can confirm or refute the claim.
Practical tools: digital forensics suites, packet analyzers like Wireshark, test harnesses, and containerized environments help reproduce results. For guidance on evaluating reviews and tool claims in the AI and tech space, FeedBuzzard’s article on evaluating AI tool reviews explains what good evidence looks like and how to read methods sections.
Validate Vulnerability Reports And Proofs Of Concept
Fact first: a vulnerability report earns trust when it pairs an explicit impact statement with a reproducible proof of concept (PoC) and remediation advice. Strong reports list a short title, affected components, attack vectors, and clear reproduction steps.
What to expect in a robust PoC: a concise script or set of commands, sample inputs, and clear expected outputs, the minimal material required for another researcher to reproduce the issue. Good PoCs avoid one-off anecdotes and instead show repeated, repeatable results across the named versions. Screenshots help but are not substitutes for code or logs.
Validation workflow: an independent analyst or the affected vendor should reproduce the issue in a controlled lab or staging instance and confirm exploitability. The final confirmation often appears as a vendor advisory, a CVE entry, or a coordinated disclosure timeline. If the reporter claims remote code execution but the PoC requires local admin and specific hardware, the impact claim is inflated.
Red flags in vulnerability reporting: missing affected versions, absence of reproduction steps, vague impact language like “could be exploited,” and failure to allow reasonable vendor response time. A problematic practice is releasing full exploitation code for high-impact vulnerabilities without a mitigation window: responsible disclosure typically coordinates with vendors first.
Practical example: a proof‑first claim that a fitness tracker exposes live location should include the device model, firmware, the API call or BLE exchange, and a short script producing the location payload. If these elements are absent, the claim remains unverified.
For readers who evaluate security claims across device categories, FeedBuzzard’s piece on IP hygiene and securing smart devices provides context on typical IoT vulnerabilities and remediation patterns.
Check Privacy Practices: Data Handling, Policies, Permissions, And Regulatory Context
Fact first: privacy claims must map to observable data flows, documented policies, and actual permission requests in apps or devices. If an article says a company does not collect location data, verify the app’s permission prompts, network traffic, and the published privacy policy.
Start with the policy. A complete privacy policy names categories of data collected, retention periods, sharing partners, and legal bases (when GDPR applies). Compare the article’s claim to the policy language. If the policy contradicts the claim, the article needs stronger evidence.
Next, inspect runtime behavior. On a phone or wearable, check permission dialogs, data-sync endpoints, and telemetry destinations. Network captures can reveal unexpected third‑party endpoints. If an article claims telemetry bypasses opt-out settings, a pcap sample or endpoint list strengthens the assertion.
Consider regulatory context. For EU users, look for lawful basis statements in the policy and data‑subject rights processes. For California, check CCPA disclosures and opt‑out mechanisms. Articles that ignore regulatory markers often miss crucial compliance signals.
Real-world nuance: an article might report a weak age‑verification system that still meets some privacy promises while failing child‑safety goals. Recent reporting highlighted how age‑verification efforts attempted technical fixes that still failed practical checks, this tension affects claims that a method is both private and effective, and is explored in reporting on age checks and verification tech in 2026. For readers assessing such tradeoffs, the TechCrunch piece on age verification illustrates how privacy promises can look good on paper yet underdeliver in practice: a useful comparison when judging real-world claims.TechCrunch analysis
Practical checklist: confirm the policy wording, capture a short network trace, inspect app permission strings, and verify data deletion or opt‑out mechanisms. For privacy toolkits and practices that creators use, FeedBuzzard’s digital privacy tools article lists utilities that help confirm data flows and permissions.
Conclusion
Insight first: trust follows verifiability. Readers should accept tech security and privacy claims only when the report provides verifiable sources, repeatable evidence, and clear privacy documentation. When a claim lacks these things, treat it as a hypothesis, not a fact.
FeedBuzzard’s coverage emphasizes transparent sourcing and practical tests: readers who apply this checklist, check authorship, demand reproducible methods, require PoCs, and confirm policies, will make better decisions about which reports to trust. This approach reduces false alarms, focuses security effort, and protects user privacy without being gullible or cynical.